A Google report particulars using AI in cyberattacks, with its Gemini chatbot being exploited by risk actors in China, North Korea, and Iran
MANILA, Philippines – Google on Friday, February 13, launched its quarterly threat intelligence report for This fall 2025, highlighting the fast-growing function that synthetic intelligence (AI) has performed in cyberattacks.
The corporate’s AI chatbot Gemini is a spotlight of the report, with the corporate figuring out the ways in which risk actors have tried to make use of the device throughout many areas comparable to social engineering, phishing, malware improvement, and data operations.
“By figuring out these early indicators and offensive proofs of idea, GTIG (Google Menace Intelligence Group) goals to arm defenders with the intelligence essential to anticipate the following part of AI-enabled threats, proactively thwart malicious exercise, and frequently strengthen each our classifiers and mannequin,” Google stated.
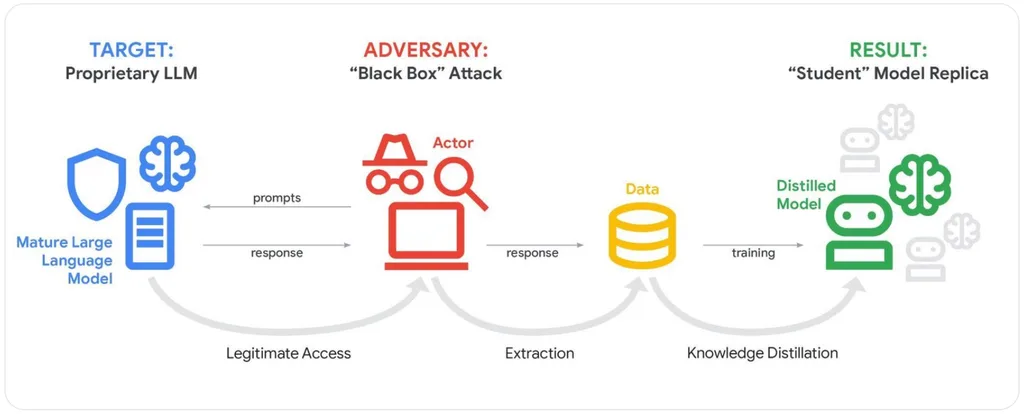
The corporate additionally discovered makes an attempt to “distill” their Gemini chatbot. “Distillation” in AI is a technique to “systematically probe a mature machine studying mannequin to extract data used to coach a brand new mannequin.”
Which means that a risk actor can construct their very own chatbot by distilling Gemini or different comparable apps, minus the standard content material era prohibitions. It primarily impacts firms constructing AI fashions reasonably than the common consumer, Google stated.
AI-enhanced phishing, malware improvement
A extra direct risk for common customers are AI-enhanced phishing and social engineering assaults.
AI smoothens out conventional phishing indicators comparable to poor grammar, awkward syntax and lack of cultural context.
“More and more, risk actors now leverage LLMs to generate hyper-personalized, culturally nuanced lures that may mirror the skilled tone of a goal group or native language,” Google stated.
Google stated that attackers at the moment are using “rapport-building phishing” which is designed to earn belief by means of “multi-turn, plausible conversations” earlier than delivering the ultimate payload.
An Iranian government-backed actor referred to as APT42 supplied Gemini with a biography of a goal, and requested it to craft a persona that may successfully lure it.
A North Korean government-backed actor, in the meantime, referred to as UNC2970, used Gemini to “synthesize OSINT (open supply intelligence or data available on-line) and profile high-value targets to assist marketing campaign planning and reconnaissance” to create “tailor-made, high-fidelity phishing personas and determine potential delicate targets for preliminary compromise.”
Except for phishing, AI-supported malware coding and power improvement have additionally been noticed by the corporate.
The Individuals’s Republic of China-based risk actor APT31 employed a “extremely structural strategy” by prompting Gemini to create an knowledgeable cybersecurity persona that may analyze programs vulnerabilities and generate focused testing plans.
Google discovered that APT31 examined a state of affairs that had the persona performing cyberattack strategies in opposition to particular US-based targets.
Two different China-based actors UNC795 and APT41, and Iran-based APT 42, used Gemini in numerous methods to assist with the creation of malicious code together with troubleshooting, information synthesis, and basically, to “speed up the event of specialised malicious instruments.”
In all of those circumstances, Google disabled the actor’s belongings thereafter on Gemini. In a single case, UNC795, the corporate discovered that “Gemini didn’t adjust to the actor’s makes an attempt to create policy-violating capabilities.”
Info operations
The GTIG additionally stated it noticed data operations actors continued to make use of Gemini for analysis, content material creation, and localization, amongst others.
“We now have recognized Gemini exercise that signifies risk actors are soliciting the device to assist create articles, generate belongings, and assist them in coding,” Google stated, however additionally they have “not recognized this generated content material within the wild.”
“For noticed IO campaigns, we didn’t see proof of profitable automation or any breakthrough capabilities. These actions are much like our findings from January 2025 that detailed how dangerous actors are leveraging Gemini for productiveness beneficial properties, reasonably than novel capabilities,” it stated.
Findings might be used to enhance Gemini’s potential to determine malicious actions to refuse requests. “Observations have been used to strengthen each classifiers and the mannequin itself, enabling it to refuse to help with such a misuse transferring ahead,” Google stated. – Rappler.com
https://weblog.passive-income4u.com/create-your-very-own-auto-publish-news-blog-site-and-earn-passive-income-in-just-4-easy-steps/
https://www.rappler.com/expertise/google-gemini-ai-threat-intelligence-report-q4-2025/