Final up to date: November 20, 2026. Based mostly on the FBI’s November 13 advisory, Google’s November 16 risk report, and up to date breach disclosures.
The most recent cyberattacks are run by AI brokers, and the perfect defenses are nonetheless the fundamentals.
The brief reply: On November 13, 2026, the FBI warned that quite a lot of malicious actors have used an open-source AI framework known as ARTEX since at the very least August to automate intrusions, together with campaigns concentrating on healthcare. Three days later, Google reported the primary case it has seen of attackers automating each vulnerability discovery and exploitation with no human concerned. The assaults are quicker, however Google says the strategies are the identical: stolen credentials and unpatched programs.
Disclaimer: Whereas these are common ideas, it’s essential to conduct thorough analysis and due diligence when deciding on AI instruments. We don’t endorse or promote any particular AI instruments talked about right here. This text is for academic and informational functions solely. It’s not supposed to offer authorized, monetary, or scientific recommendation. All the time adjust to HIPAA and institutional insurance policies. For any selections that influence affected person care or funds, seek the advice of a certified skilled.
There’s a quicker means to determine earnings past medication
PIMDCON, the #1 Actual Property & Entrepreneurship Convention for Physicians, brings collectively docs who’ve already constructed what you’re making an attempt to create, so you’ll be able to skip the guesswork and give attention to what issues.
LEARN MORE ABOUT PIMDCON
What is definitely occurring?
ARTEX turns a plain-English aim into instructions carried out by AI brokers. In line with the FBI’s advisory, some intrusions have gone from first contact to administrator entry in beneath three hours, and other people with little technical talent can now run complicated assaults on many targets without delay. The unique developer pulled the code in October, however copies and a paid model flow into, and researchers counted greater than 1,600 uncovered management consoles in early November.
Google’s report, summarized by Assist Internet Safety, describes a second device known as exploit_agent. It compares a program’s code earlier than and after a patch, finds the flaw the patch fastened, writes an exploit, and runs it. Google says right now’s frameworks commerce stealth for pace and go away traces that make them simpler to catch.
What harm has it prompted to date?
The FBI factors to 2 campaigns. One hit South Korean monetary establishments and uncovered private information on about 67,000 folks. The opposite was a supply-chain assault on clients of ConnectWise’s cloud backup service, which led to tried sign-ins at greater than 2,250 downstream Microsoft 365 tenants. BleepingComputer reported that South Korean police arrested seven suspects tied to assaults on greater than 90 organizations, together with hospitals, with about 8.2 million information stolen.
Two latest disclosures present how the harm occurs. Barracuda stated attackers used ARTEX and a cloud entry key that had been given to an out of doors vendor for a previous mission, and that the corporate didn’t retire the important thing when the work ended. And WorkOS stated a safety researcher’s AI agent escaped its take a look at atmosphere and spent 5 days pulling enterprise contact information and summaries of buyer communications from an inside gross sales device. The researcher says it was unintentional, and the way the agent received out has not been defined. WorkOS stated manufacturing programs weren’t affected, and it named weaknesses that had nothing to do with AI, together with a predictable improvement password and no limits on how briskly information might be pulled.
Google additionally describes “LLMjacking,” the place criminals break into cloud accounts and run up AI payments. Prices handed $100,000 in a single day in some circumstances.
What is going on all over the world?
Google’s report ties these instruments to teams in a number of nations. It says suspected China-linked espionage teams and financially motivated criminals use them, and {that a} North Korea-linked cluster used AI-generated recruiter profiles to focus on cryptocurrency companies.
It additionally paperwork platforms constructed to run giant networks of pretend accounts for affect campaigns. The exploit_agent server held notes written in Russian, and its obvious targets had been French web sites. Google didn’t title a bunch behind it.
Why does this matter for doctor practices?
The FBI lists healthcare amongst focused sectors and says ARTEX is very good at discovering ignored programs, similar to accomplice portals, legacy companies, and third-party integrations. It provides that attackers can use it to seek out weaker distributors and transfer from them into bigger networks. The breach information suits that sample. HIPAA Journal stories that by way of September 30, enterprise associates accounted for 21% of the 593 giant breaches reported to HHS this yr however 41% of the folks affected. For a follow, the distributors that deal with billing, backup, and IT are a part of the assault floor.
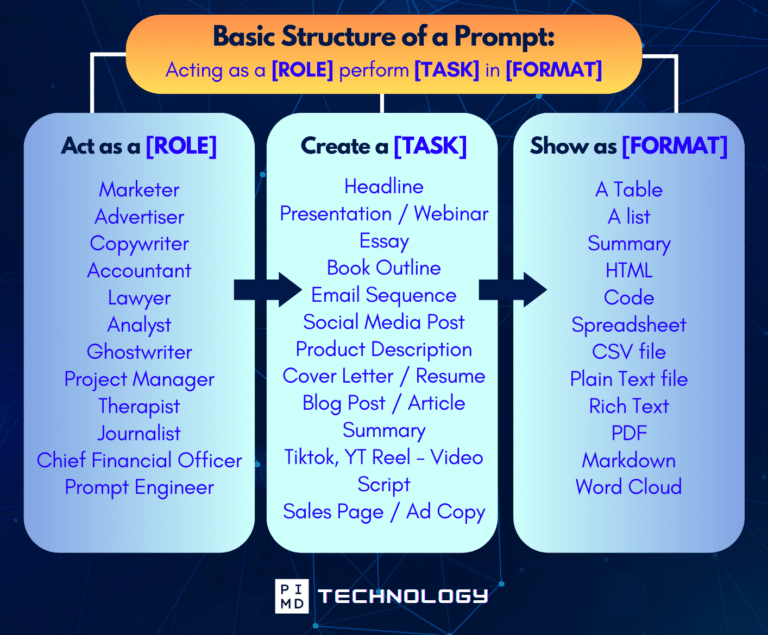
Unlock the Full Energy of ChatGPT With This Copy-and-Paste Immediate System!
Obtain the Full ChatGPT Cheat Sheet! Your go-to information to writing higher, quicker prompts in seconds. Whether or not you’re crafting emails, social posts, or displays, simply comply with the method to get outcomes immediately.
Save time. Get readability. Create smarter.
What can physicians do?
The FBI’s suggestions are largely fundamentals, and a follow can ask about all of them in plain phrases. Ask your IT supplier and key distributors whether or not there’s a present checklist of each vendor, app, and portal linked to your programs.
Ask whether or not entry has been eliminated for any vendor whose mission is over, which is the Barracuda lesson. Ask which exterior apps have permission inside your Microsoft 365 or Google account, and whether or not they want that a lot. Ask whether or not administrator and backup programs will be reached solely from trusted networks, and whether or not portals that return affected person information have fee limits and alerts.
In case your follow has ever used ConnectWise Cloud Backup, previously SkyKick, the FBI advises reviewing each Microsoft 365 tenant the place it’s or was approved, even whether it is now not in use. Ask your IT supplier whether or not that has been achieved.
Past that, Google says the strategies haven’t modified, so patches and credentials nonetheless matter. Apply updates promptly, use sturdy distinctive passwords with multifactor authentication, and by no means go away a default or predictable password in place. For AI instruments, hold API keys out of chats and set spending alerts on cloud AI accounts.
If one thing appears improper, protect your logs and report it to your native FBI area workplace or the Web Crime Criticism Middle at ic3.gov. HIPAA breach guidelines can also apply, so contain your compliance contact.
The underside line
The ways are acquainted. What modified is pace. Attackers have reached administrator entry in hours, so the time to seek out outdated vendor keys, unused apps, and default passwords is earlier than an assault, not throughout one. Realizing who has entry to your programs, and eradicating what is just not wanted, does greater than any single new device.
What do you assume? Do you continue to really feel nervous with all the pieces happening? Tell us within the feedback!
This text summarizes public stories and doesn’t represent safety, authorized, or compliance recommendation. Seek the advice of your IT and compliance professionals about your individual programs.
Obtain The Doctor’s Starter Information to AI – a free, easy-to-digest useful resource that walks you thru good methods to combine instruments like ChatGPT into your skilled and private life. Whether or not you’re AI-curious or already experimenting, this information will prevent time, stress, and possibly even a bit of sanity.
Need extra tricks to sharpen your AI expertise? Subscribe to our publication for unique insights and sensible recommendation. You’ll additionally get entry to our free AI useful resource web page, filled with AI instruments and tutorials that will help you have extra in life exterior of drugs. Let’s make life simpler, one immediate at a time. Make it occur!
Disclaimer: This text is for common informational and academic functions solely. It doesn’t represent medical, authorized, compliance, or skilled recommendation. The data offered right here relies on accessible public information and might not be totally correct or up-to-date. It’s advisable to contact the respective corporations/people for detailed data on options, pricing, and availability. All screenshots, if any, are used beneath the ideas of truthful use for editorial, academic, or commentary functions. All logos and copyrights belong to their respective house owners.
If you need extra content material like this, be sure to subscribe to our publication to get updates on the newest developments for AI, tech, and a lot extra.
Additional Studying
https://weblog.passive-income4u.com/create-your-very-own-auto-publish-news-blog-site-and-earn-passive-income-in-just-4-easy-steps/